Malicious Claude Opus 5 Desktop App Serves Up Credential‑Stealing RevStealer Malware
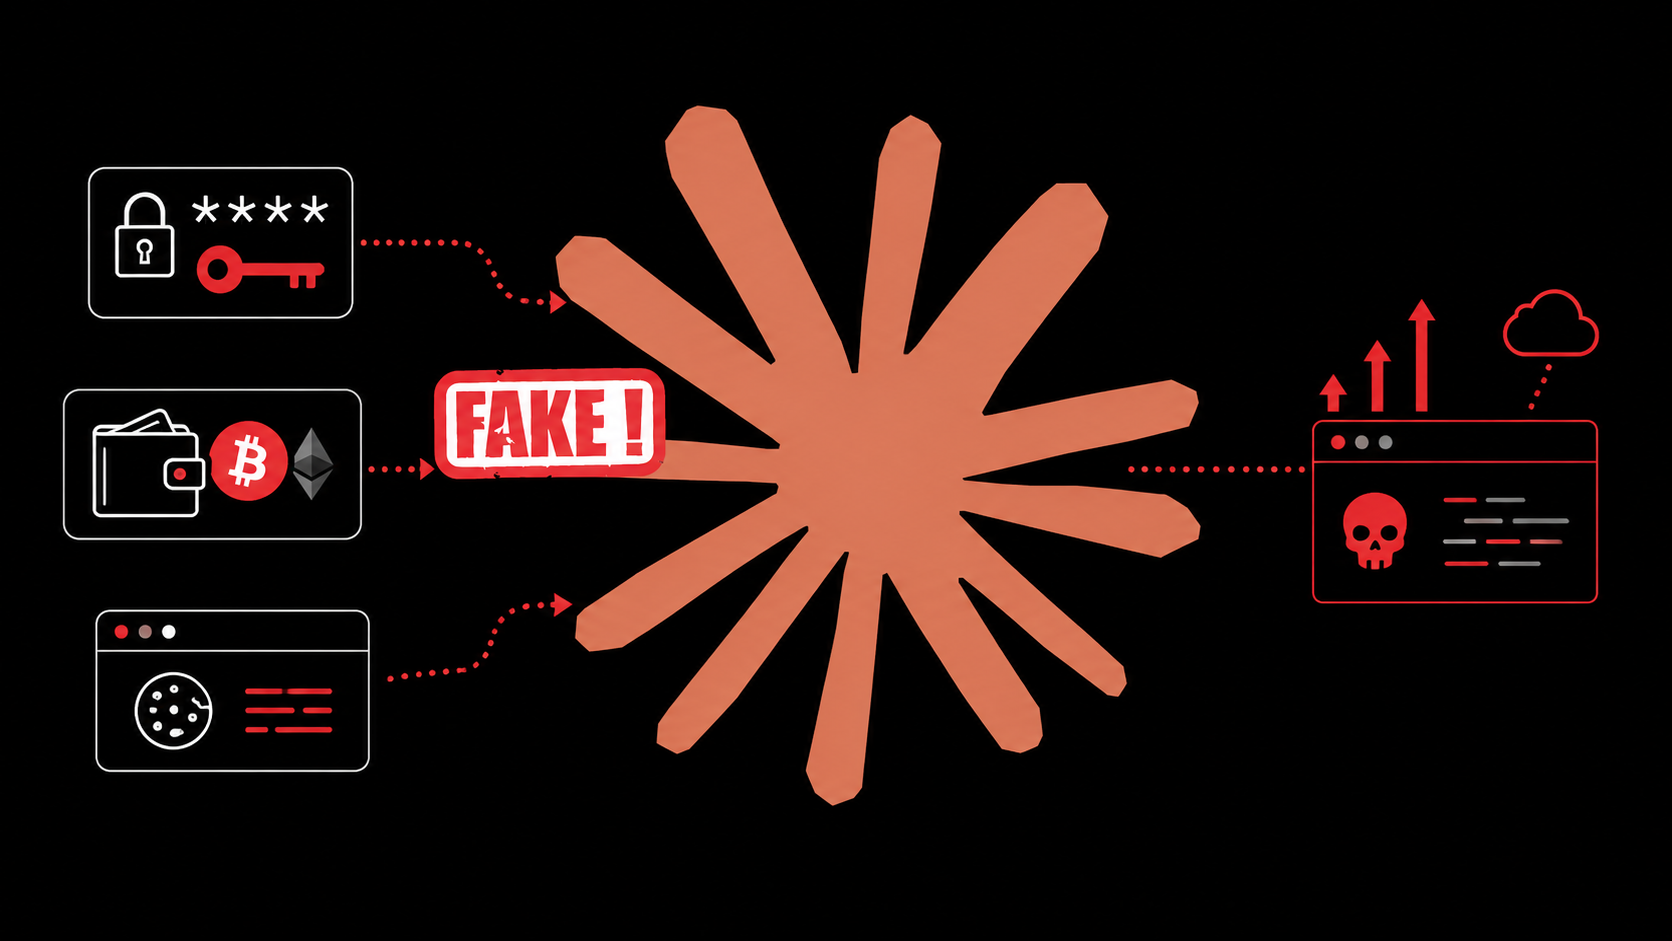
Cybersecurity researchers have identified a new campaign that disguises a credential‑stealing tool as a free desktop version of Anthropic's Claude Opus 5, a popular generative AI model. The malicious package, built on the Electron framework, installs RevStealer, a Windows‑focused information stealer that can capture passwords, cryptocurrency wallet files and browser session data.
Threat actors are leveraging the surge in demand for AI‑powered applications to lure users into downloading the counterfeit software. By mimicking the look and feel of an official Claude Opus 5 client, the trojanized installer convinces unsuspecting users that they are obtaining a legitimate productivity tool, while silently deploying the hidden payload.
RevStealer, which has appeared in previous campaigns, is designed to operate stealthily on compromised machines. Once installed, it enumerates stored credentials from browsers, password managers and cryptocurrency wallets, then exfiltrates the data to command‑and‑control servers controlled by the attackers. The malware also harvests active session cookies, enabling further account takeover without requiring additional passwords.
The use of Electron for the fake Claude Opus 5 client is noteworthy because the framework packages web technologies into a single executable, making it easier for adversaries to embed malicious code while preserving a polished user interface. This approach complicates detection, as the resulting binary can appear benign to both users and some security tools that focus on more traditional Windows executables.
Security analysts recommend that users verify the source of any AI desktop applications and avoid downloading software from unofficial sites or peer‑to‑peer networks. Organizations should ensure endpoint protection solutions are configured to flag unknown Electron applications and monitor for the network traffic patterns associated with RevStealer’s data exfiltration. As the appetite for generative AI tools continues to grow, experts warn that similar masquerading schemes are likely to proliferate, underscoring the need for heightened vigilance and robust cybersecurity hygiene.



Comments (0)
Be the first to comment.
Join the discussion