Cybercriminals Exploit Polygon Blockchain to Conceal Malware Command Network and Harvest Bank Data
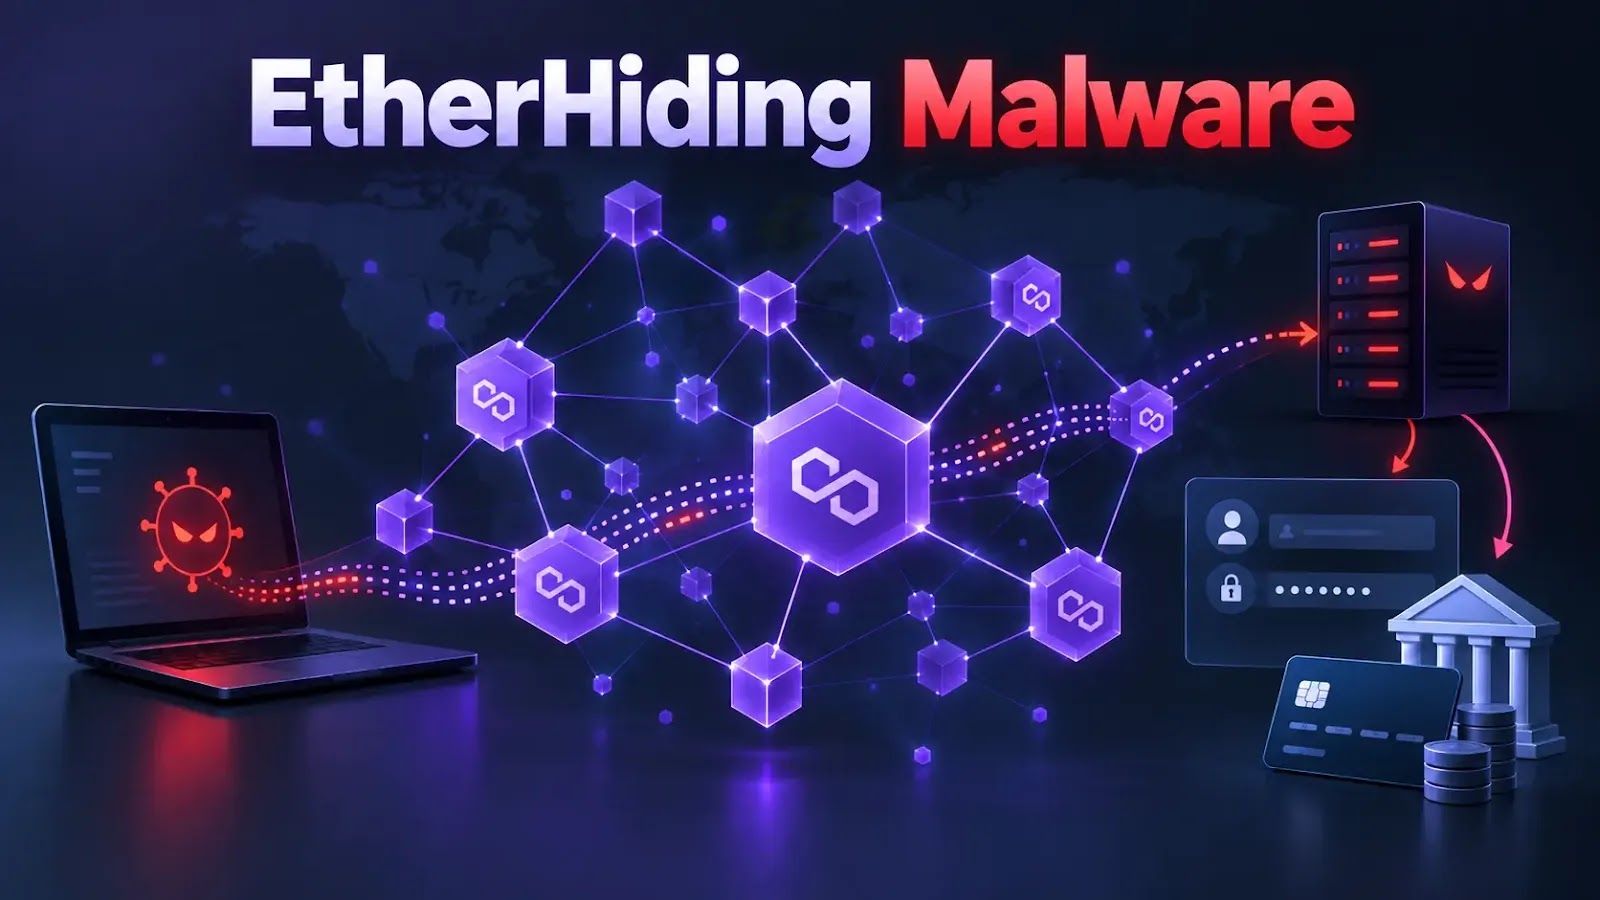
A newly identified malware campaign dubbed EtherHiding is leveraging the Polygon blockchain as a covert command-and-control (C2) platform, enabling operators to shift their infrastructure without altering the malicious code already installed on victim computers. Security researchers say the technique, first observed in activity dating back to November, allows the threat actors to remain agile and evade traditional detection methods that focus on static network indicators.
EtherHiding embeds instructions and cryptographic keys within transactions on Polygon, a layer‑2 scaling solution for Ethereum. By reading these blockchain entries, infected hosts can retrieve updated commands, download additional payloads, or exfiltrate stolen banking credentials. Because blockchain data is publicly replicated across numerous nodes, the malicious traffic blends with legitimate network activity, making it difficult for defenders to pinpoint malicious communications.
The use of a public blockchain for C2 is not unprecedented, but the choice of Polygon marks a shift toward platforms that offer lower transaction fees and faster confirmation times than Ethereum’s mainnet. Researchers note that the malware’s payload does not need to be recompiled when the operators change servers or domains; instead, they simply post new instructions to the blockchain, and the compromised machines automatically adapt. This dynamic reduces the operational overhead for the attackers and complicates takedown efforts.
Banking credential theft remains the primary goal of EtherHiding. Once the malware gains access to a victim’s system, it deploys keyloggers and credential‑stealing modules that capture login details for online banking portals. The stolen data is then routed through encrypted channels to the attackers’ infrastructure, often via anonymizing services. By coupling credential theft with a resilient C2 backbone, the campaign can sustain prolonged campaigns against financial targets without interruption.
Cybersecurity firms warn that the emergence of blockchain‑based C2 channels could herald a broader trend among financially motivated cybercriminals. Traditional network monitoring tools may miss these covert communications, prompting a need for deeper analysis of blockchain transaction patterns and the development of specialized detection heuristics. While the public nature of blockchain data offers transparency, it also provides a cover that malicious actors are increasingly exploiting.
Experts suggest that organizations should strengthen endpoint monitoring, enforce multi‑factor authentication for banking services, and consider integrating blockchain analytics into their threat‑intelligence workflows. As the EtherHiding operation continues to evolve, law‑enforcement and security communities are urged to collaborate on identifying the operators behind the campaign and to develop coordinated strategies to disrupt their use of decentralized infrastructure.
The discovery, originally reported by the GBHackers research collective, underscores the adaptive nature of modern malware and the challenges posed by emerging technologies that can be repurposed for illicit activities. Ongoing investigations aim to map the full scope of the campaign, assess its impact on financial institutions, and explore mitigation techniques that can counteract the stealth afforded by blockchain‑based command networks.



Comments (0)
Be the first to comment.
Join the discussion