Cyber Intrusions Target Texas‑Bound Oil Tankers, Prompt Coast Guard and FBI Intervention
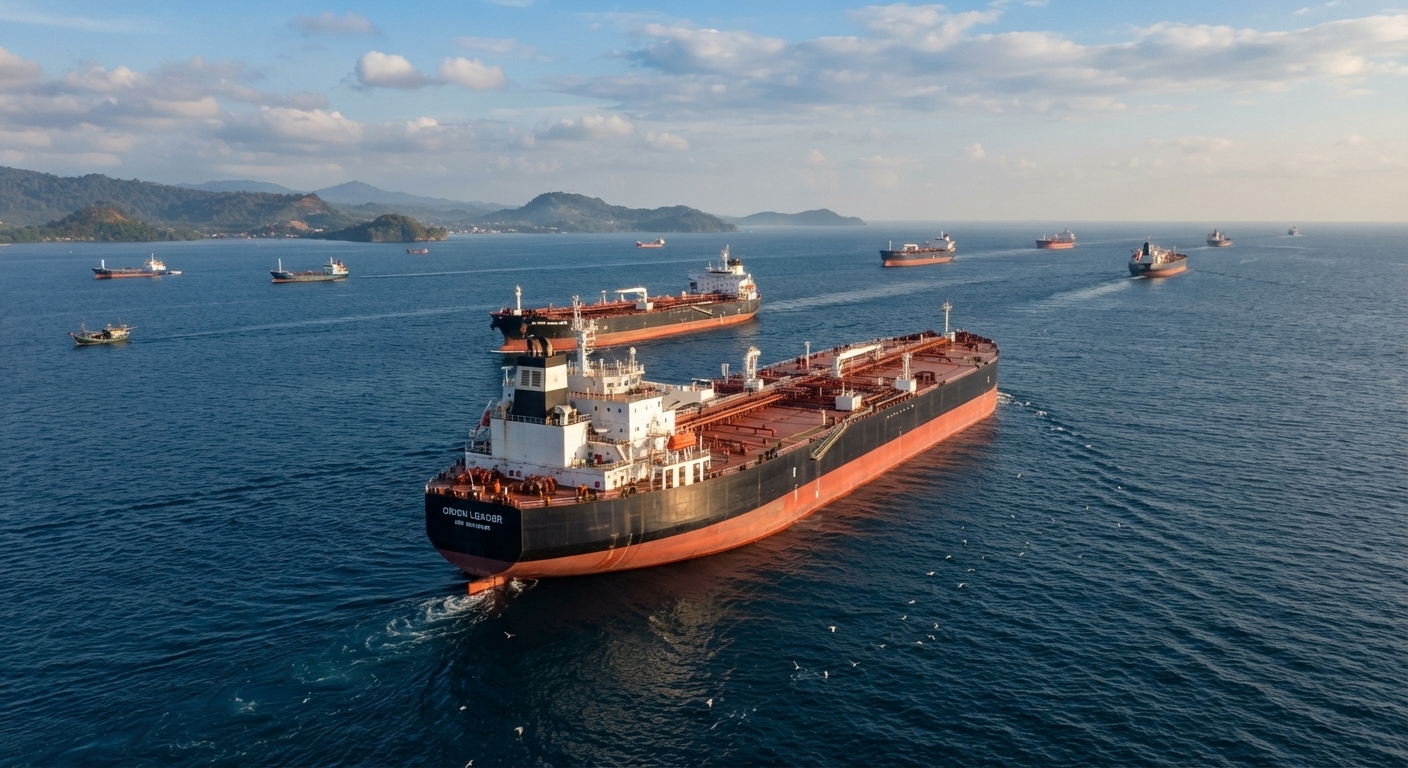
U.S. authorities intervened last month after two oil tankers bound for Texas experienced cyber intrusions that threatened their navigation and onboard control systems. Coast Guard personnel, accompanied by FBI agents, boarded the vessels to assess the breach and secure the ships before they could reach port.
The incidents underscore a growing vulnerability in the maritime sector, where increasing reliance on digital networks makes vessels susceptible to remote manipulation. In both cases, the attackers reportedly accessed shipboard computers that manage navigation, engine control and communications, raising concerns about the potential for loss of vessel control, environmental spills, or disruptions to port operations.
Maritime cyber‑security experts note that modern tankers are equipped with integrated systems that share data across satellite links, onboard sensors and shore‑based monitoring platforms. While this connectivity improves efficiency, it also expands the attack surface for malicious actors. The recent attacks illustrate how a breach in one system can cascade, affecting critical functions such as steering, propulsion and cargo handling.
Federal officials have not disclosed the identity of the perpetrators or the specific malware used, but they emphasized that the incidents were isolated and that no immediate safety hazards were reported. The rapid response by the Coast Guard and FBI, however, reflects heightened vigilance after high‑profile cyber events in other industries, including the 2017 NotPetya attack that crippled a major global shipping line.
Industry groups have long warned that the maritime domain lags behind other sectors in cyber‑risk mitigation. The International Maritime Organization (IMO) has issued guidelines urging ship owners to adopt robust cybersecurity management systems, but implementation varies widely. The U.S. Department of Homeland Security has recently increased funding for maritime cyber‑defense training and for the development of threat‑intelligence sharing platforms between the private sector and government agencies.
Looking ahead, regulators are expected to tighten oversight of vessel cybersecurity, potentially mandating regular vulnerability assessments and stricter controls over remote access. For ship operators, the incidents serve as a reminder to prioritize network segmentation, patch management and crew awareness. As global trade continues to depend on a seamless flow of energy commodities, safeguarding the digital backbone of maritime infrastructure remains a critical priority for both national security and economic stability.



Comments (0)
Be the first to comment.
Join the discussion