Cyber Intrusion Forces French Blood Service to Halt Operations at Three Refrigeration Sites
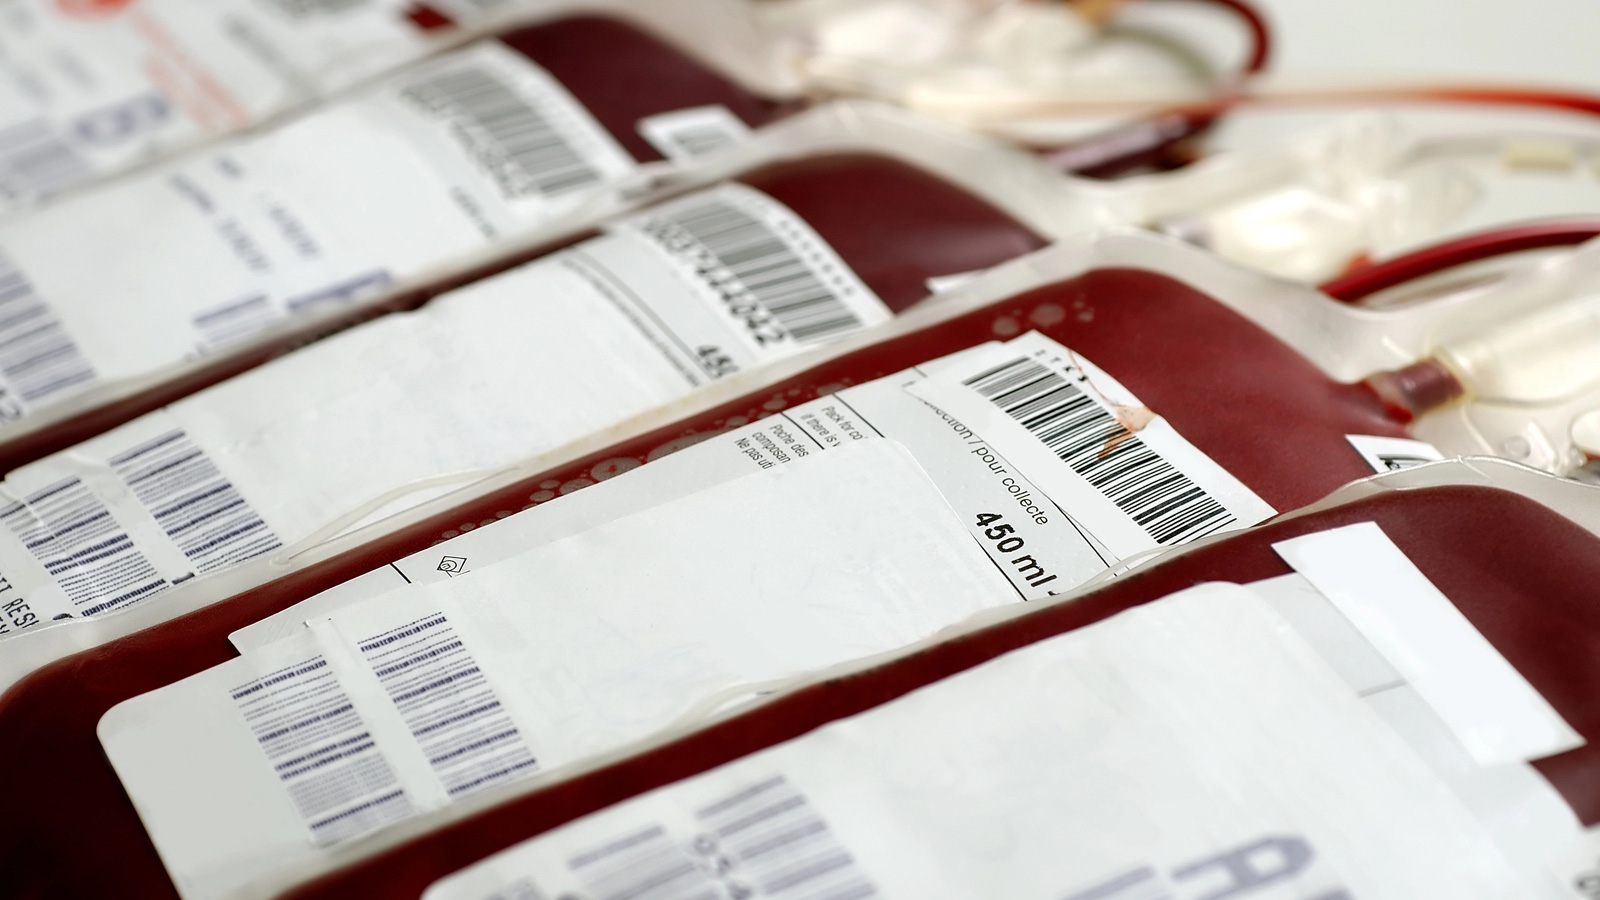
France's national blood service confirmed that a cyberattack on a refrigeration equipment supplier altered temperature and defrost settings at three of its blood storage facilities, jeopardizing the integrity of the blood products held there.
The agency swiftly moved to isolate the affected units, diverting temperature-sensitive supplies to alternative storage locations while technicians inspected the equipment for signs of tampering. Officials emphasized that no immediate shortage of blood for hospitals has been reported, but the incident highlighted a vulnerable point in the supply chain.
Blood must be kept within a narrow temperature range—typically between 2°C and 6°C—to remain viable for transfusion. Any deviation, especially an unintended rise in temperature or an unscheduled defrost cycle, can compromise clotting factors and reduce shelf life, forcing disposal of the product. The cyber intrusion therefore posed a direct risk to the safety and availability of lifesaving blood components.
Cyber threats to health‑care infrastructure have been on the rise, with attackers increasingly targeting the software that controls medical devices and supporting equipment. By compromising a third‑party refrigeration provider, the perpetrators were able to influence multiple storage sites simultaneously, illustrating how supply‑chain dependencies can amplify the impact of a single breach.
In response, the blood service activated its emergency protocols, which include redundant refrigeration units, temperature‑monitoring alarms, and a rapid‑response logistics network. These safeguards are designed to limit product loss and maintain continuous supply to hospitals, even when primary systems fail.
French health authorities have launched an investigation in coordination with law‑enforcement cyber units to identify the attackers and assess the full extent of the breach. Preliminary findings suggest the intrusion exploited a remote access vulnerability in the equipment provider's control software, a scenario that regulators say underscores the need for stricter cybersecurity standards across medical supply chains.
Looking ahead, the blood service plans to conduct a thorough audit of all connected equipment, upgrade authentication mechanisms, and work with the refrigeration vendor to patch vulnerable systems. Industry observers note that such incidents may prompt broader legislative action aimed at securing critical health‑care infrastructure against digital sabotage.
Comments (0)
Be the first to comment.
Join the discussion