SonicWall Warns of Active Exploitation Targeting SMA 1000 Appliances
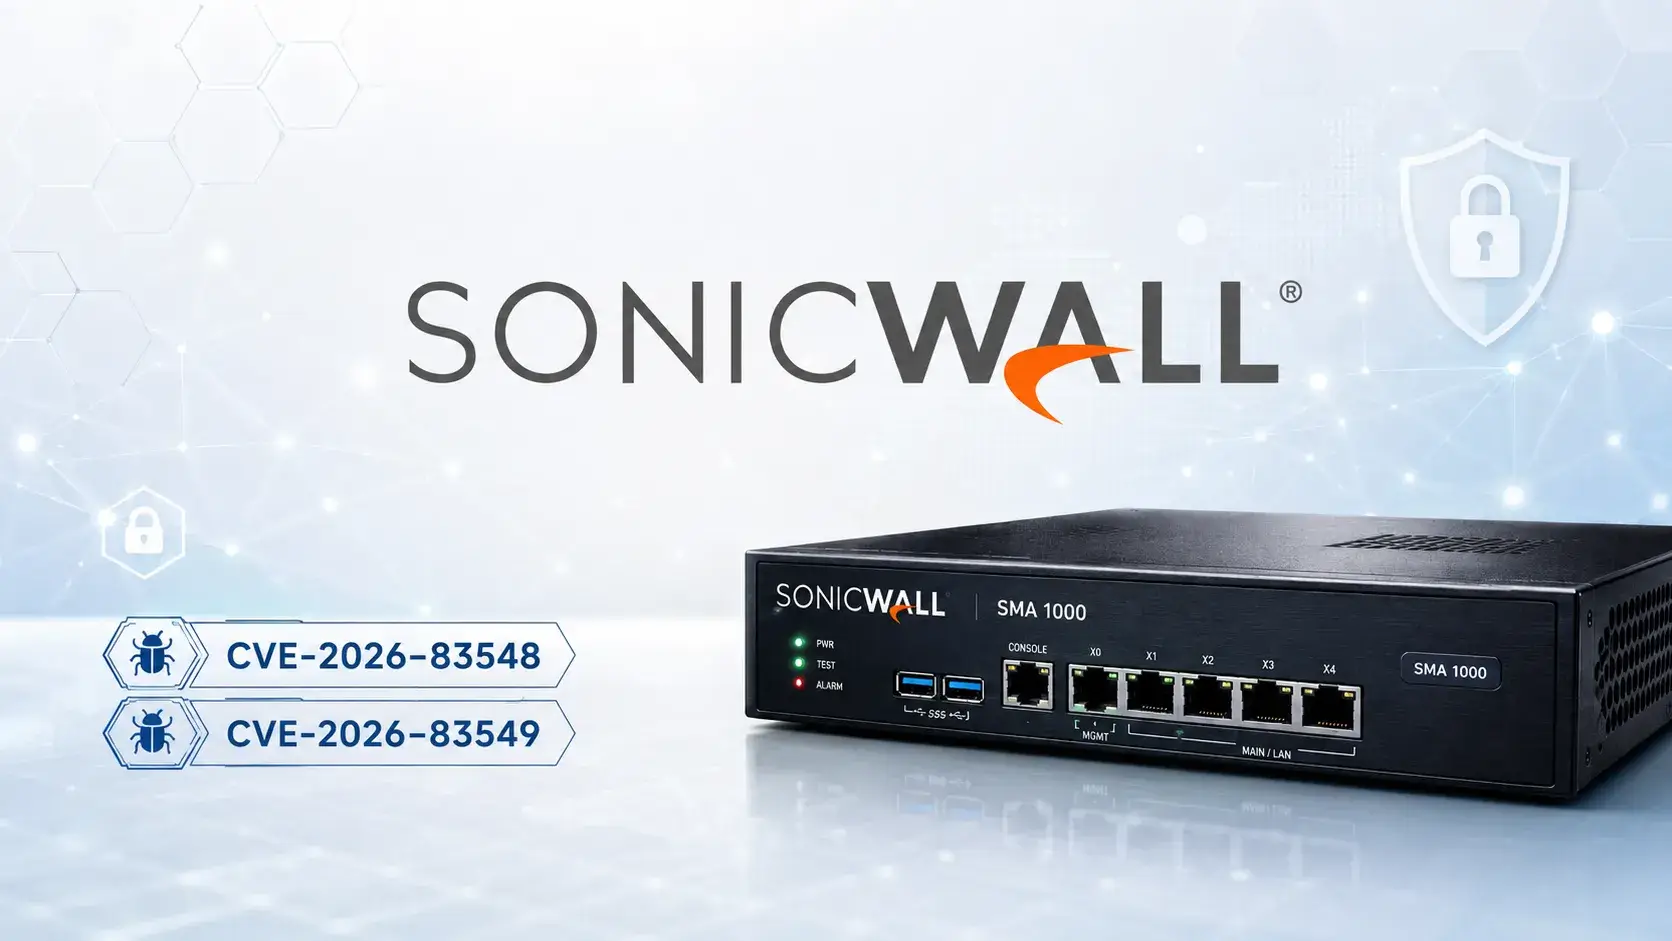
SonicWall has released an urgent security advisory alerting customers to two critical flaws in its SMA 1000 Series secure access appliances, noting that evidence points to active exploitation in the wild.
The vulnerabilities, catalogued as CVE-2026-83548 and a second, related CVE, affect the core firmware that governs remote access, authentication and traffic inspection. According to the advisory, attackers can leverage these weaknesses to bypass authentication mechanisms and gain unauthorized access to internal networks protected by the devices.
The SMA 1000 line is widely deployed in midsize and enterprise environments to provide secure remote connectivity for employees, partners and managed service providers. Because the appliances often sit at the network perimeter, a successful breach can open a path to sensitive data, internal services and potentially facilitate further lateral movement across an organization’s infrastructure.
SonicWall recommends that administrators apply the vendor‑provided firmware updates immediately and review configuration settings to ensure that default credentials have been replaced and that strong, multi‑factor authentication is enforced for remote users. The company also advises customers to monitor logs for unusual login attempts and to isolate any compromised devices pending remediation.
Industry analysts note that the timing of the advisory aligns with a broader trend of attackers focusing on network edge devices, which historically receive less frequent patching than end‑point systems. The public disclosure of active exploitation raises the urgency for organizations to reassess their patch management processes and to consider compensating controls, such as network segmentation and intrusion detection, while awaiting full remediation.
The advisory, originally reported by the security research collective GBHackers, underscores the importance of rapid response to emerging threats. As more details emerge, SonicWall has pledged to continue sharing indicators of compromise and to work with partners in the security community to mitigate the impact of the attacks.



Comments (0)
Be the first to comment.
Join the discussion