Cling Botnet Cloaks C2 Traffic as Google STUN to Hijack IoT Devices
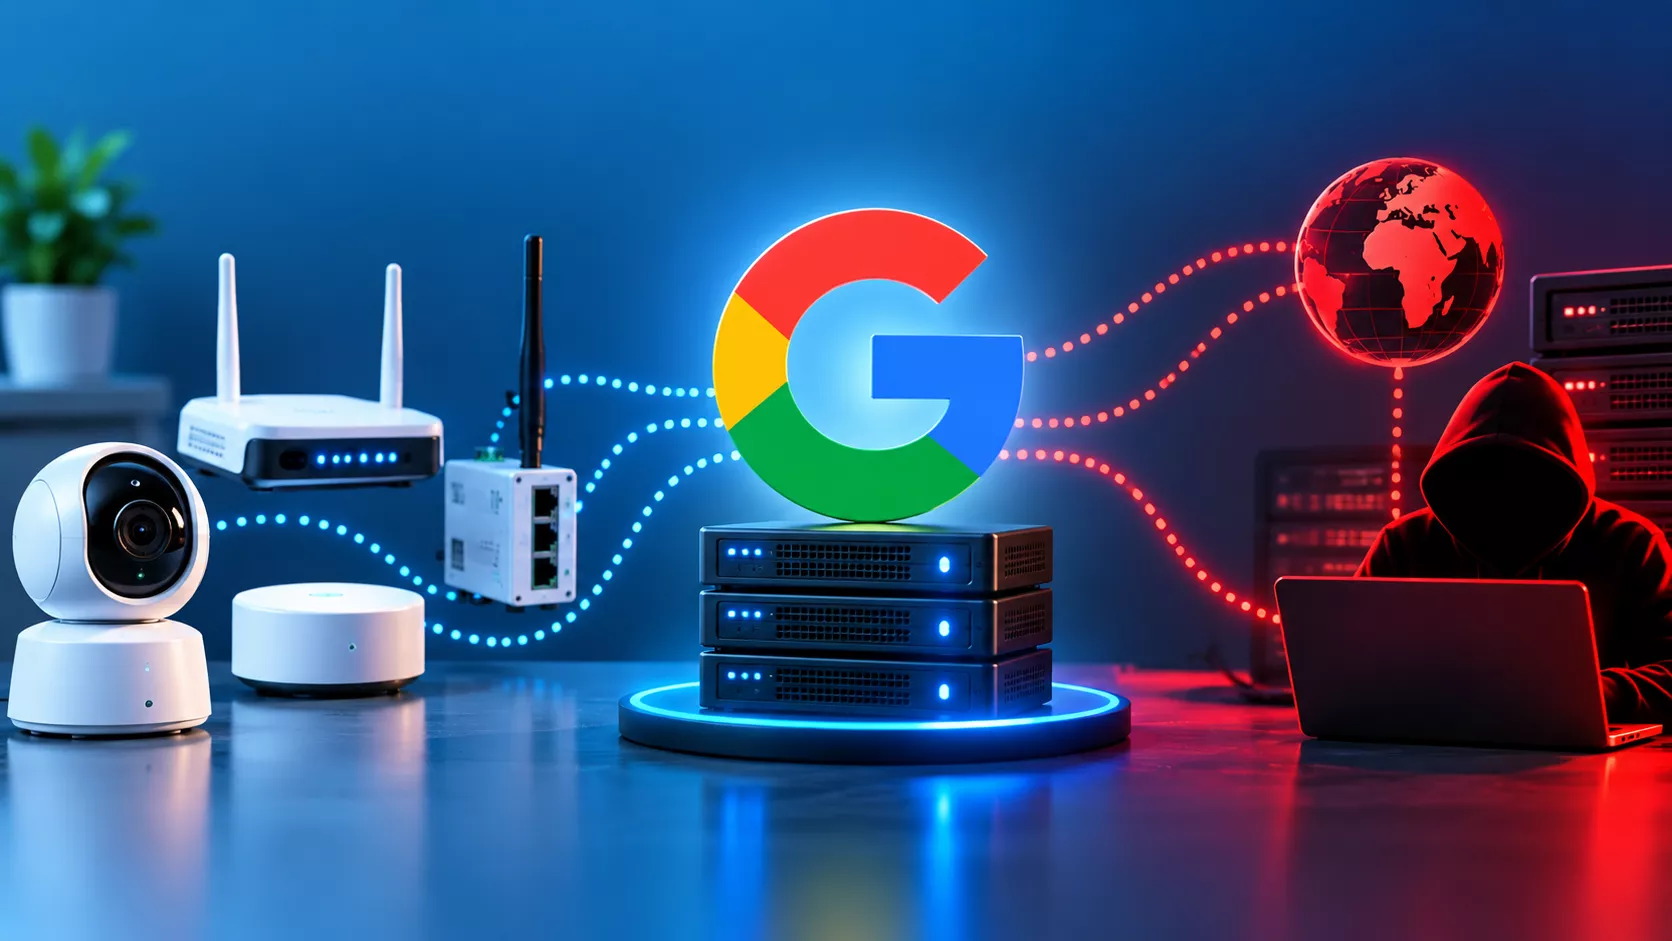
A newly discovered IoT botnet dubbed Cling is evading detection by disguising its command‑and‑control (C2) traffic as legitimate Session Traversal Utilities for NAT (STUN) packets, even mimicking traffic that appears to come from Google’s public STUN servers.
STUN is a widely used protocol that helps devices behind NAT routers discover their public IP address and negotiate connections for real‑time communications. By forging STUN‑like headers and routing packets through IP ranges owned by Google, the malware blends its malicious traffic with benign network flows, making it difficult for conventional intrusion‑detection systems to flag the activity.
The botnet targets internet‑facing devices such as cameras, routers and smart appliances that often run outdated firmware and lack robust authentication. Once compromised, the devices receive encrypted instructions hidden inside the faux STUN packets, allowing attackers to launch coordinated actions ranging from distributed denial‑of‑service attacks to credential harvesting across the compromised pool.
Security researchers who first reported the threat, known as GBHackers, note that the technique represents an evolution in IoT‑focused malware. By piggybacking on a trusted service, Cling sidesteps many network‑level defenses that rely on known malicious IP addresses or signature‑based detection. Analysts are now urging organizations to deploy deeper packet inspection and behavioral analytics that can identify anomalies in STUN traffic patterns, such as unexpected payload sizes or irregular timing.
Mitigation efforts focus on hardening vulnerable devices, enforcing regular firmware updates, and restricting outbound traffic to only required services. As the IoT ecosystem continues to expand, experts warn that similar masquerading tactics could become more common, prompting a shift toward more context‑aware security controls and collaborative threat‑intelligence sharing among vendors and researchers.

Comments (0)
Be the first to comment.
Join the discussion