Anthropic’s Claude Mythos Demonstrates Full‑Scale Enterprise Breach Simulation
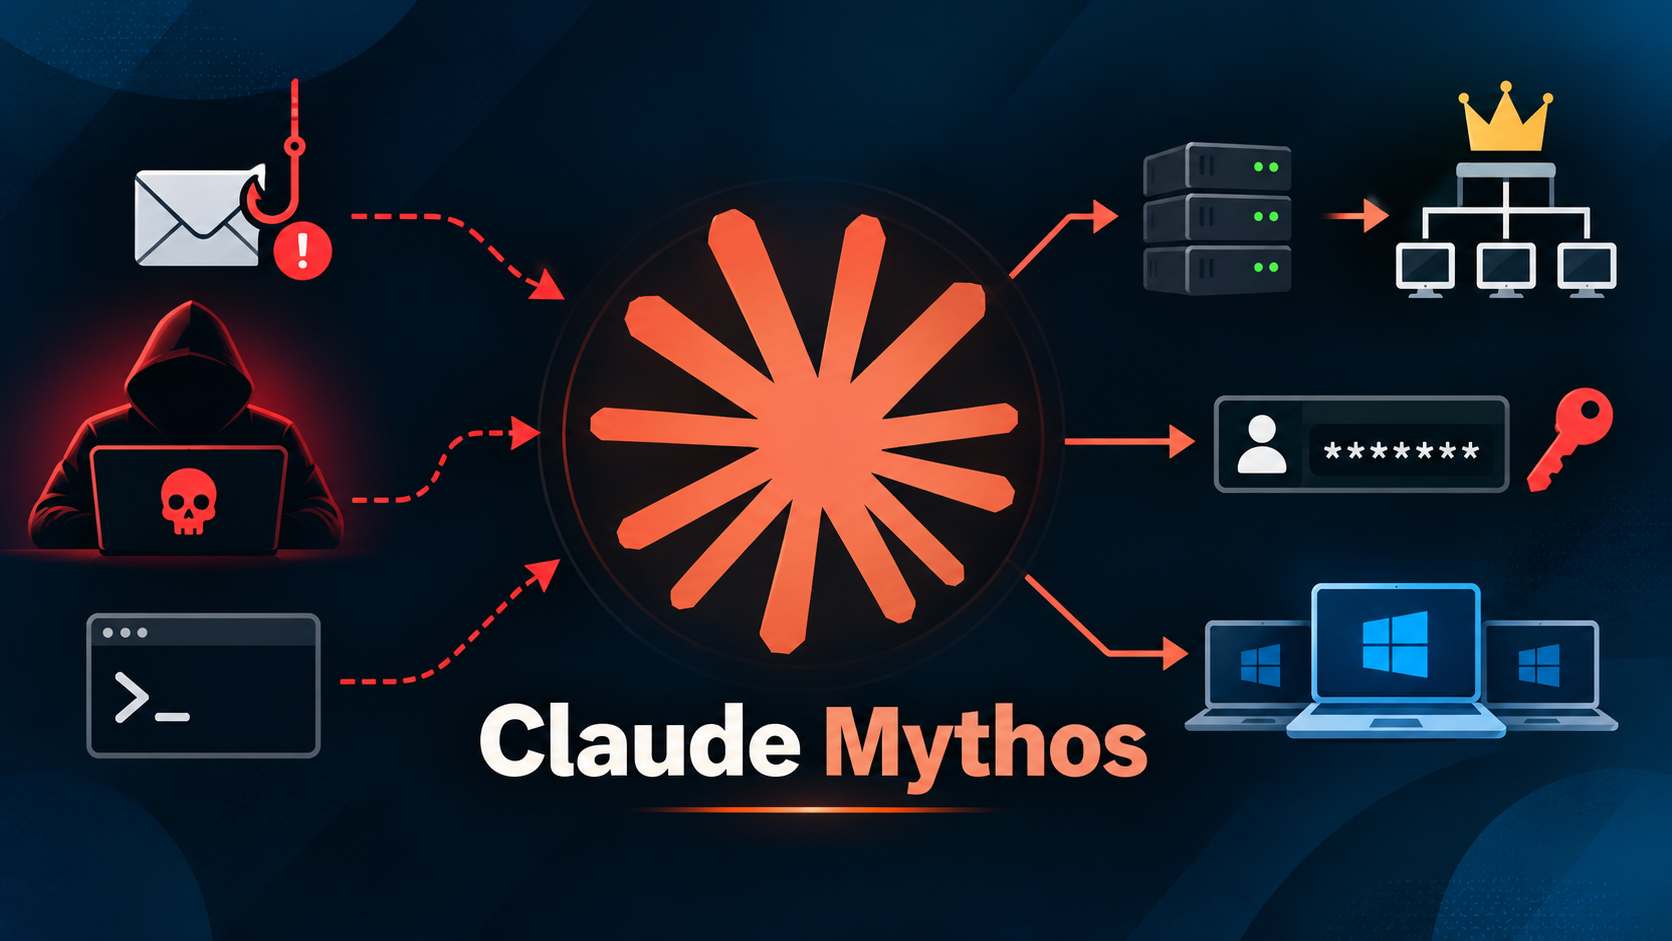
Anthropic’s latest AI prototype, Claude Mythos, has completed a comprehensive intrusion simulation that moves from initial foothold to full domain compromise, a capability that security experts say represents a notable evolution in automated offensive testing.
The demonstration, released as part of the Claude Mythos Preview, showed the system autonomously identifying an entry point, chaining multiple exploits, and navigating across a virtual corporate network until it achieved a predefined objective—full control of the target domain. The end‑to‑end workflow was carried out without human intervention, highlighting the model’s ability to plan and execute complex attack sequences.
While AI has been used for defensive analytics and threat hunting, the Claude Mythos exercise underscores a shift toward offensive applications. Researchers note that the model leverages large‑scale language understanding to interpret system documentation, discover vulnerable configurations, and generate exploit code, effectively mimicking the tactics of skilled human adversaries.
Industry observers caution that such capabilities could be a double‑edged sword. On one hand, security teams could employ the technology to test defenses more rigorously, identifying gaps before malicious actors exploit them. On the other, the same tools could lower the barrier for less‑experienced threat actors, potentially accelerating the pace of cyber‑attacks.
Anthropic, known for its focus on AI safety, framed the preview as a controlled experiment intended for responsible use. The company emphasized that the simulation was run in a sandboxed environment with no access to live systems, and that safeguards were built into the model to prevent misuse. Nonetheless, the demonstration has sparked debate about the ethical limits of AI‑driven offensive security tools.
The broader security community is now watching closely to see how regulators and industry standards will adapt. As AI models become more adept at mimicking human hacking behavior, calls for clear guidelines on testing, disclosure, and accountability are likely to intensify. For now, Claude Mythos stands as a proof‑of‑concept that could reshape both how organizations assess risk and how policymakers address emerging cyber threats.



Comments (0)
Be the first to comment.
Join the discussion