U.S. Cyber Agencies Issue Alert on Vulnerabilities in Industrial Refrigeration Controllers
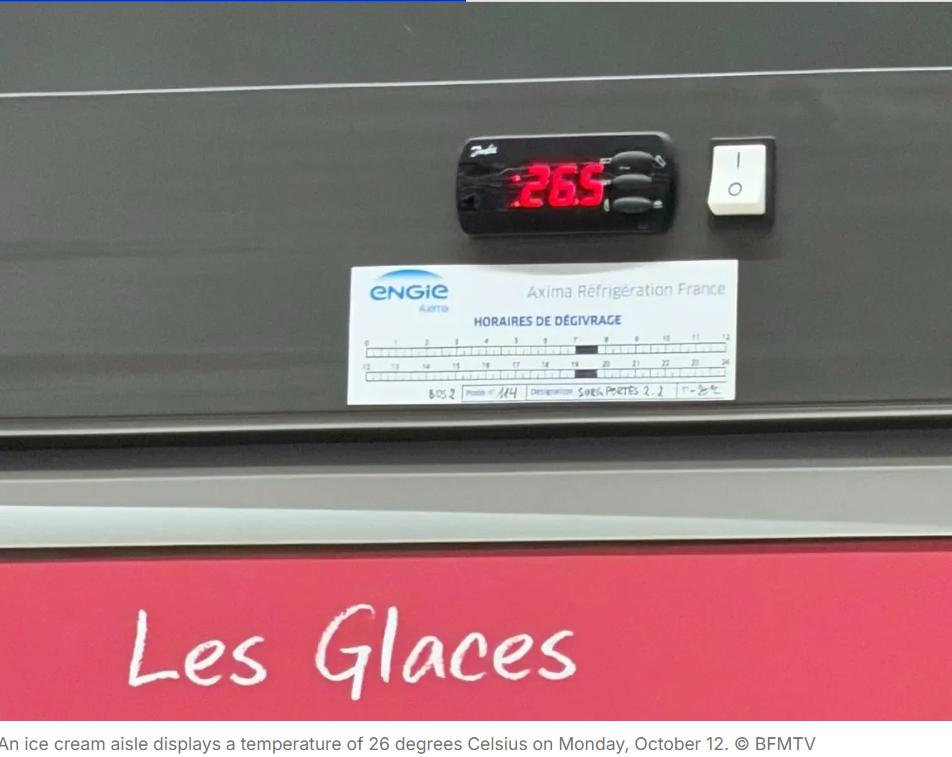
Federal cybersecurity authorities have issued a joint advisory warning that attackers are increasingly targeting the control systems that regulate industrial refrigeration equipment. The alert, signed by the Cybersecurity and Infrastructure Security Agency (CISA), the Federal Bureau of Investigation (FBI), the Department of Health and Human Services (HHS), the U.S. Department of Agriculture (USDA) and the Department of Transportation (DOT), highlights that many of the vulnerabilities can be mitigated with straightforward steps, the most effective of which is to remove the controllers from public networks.
Industrial refrigeration controllers are a critical component of the cold‑chain infrastructure that keeps food, pharmaceuticals and other temperature‑sensitive products safe. Because these devices often run on legacy operating systems and are deployed with default passwords, they present an attractive attack surface for cybercriminals seeking to disrupt supply chains, extort operators or cause physical damage. Recent incidents involving other operational technology (OT) environments, such as water treatment plants and manufacturing lines, have shown how quickly a modest intrusion can cascade into broader operational failures.
The advisory outlines a series of immediate actions for facility operators. First, any controller that does not require remote access should be isolated from the internet and placed on a segregated network. Second, organizations are urged to apply available firmware updates, replace default credentials, and enable multi‑factor authentication where possible. Third, continuous monitoring for anomalous traffic and regular vulnerability scans are recommended to detect attempts at exploitation before they succeed.
Beyond technical remediation, the agencies stress the importance of coordinated response planning. Operators are encouraged to develop incident‑response playbooks that involve both IT and OT teams, and to establish communication channels with federal partners should a breach be suspected. The advisory also points to resources hosted on the CISA website, including templates for network segmentation and guidance on securing industrial control systems.
Looking ahead, officials indicate that this advisory may be the first of a series aimed at hardening the nation’s food‑safety infrastructure against cyber threats. While no specific regulatory changes have been announced, the joint effort signals a growing recognition that the security of refrigeration controllers is a matter of public health and economic stability. Stakeholders are expected to monitor forthcoming updates from the participating agencies as the threat landscape evolves.


Comments (0)
Be the first to comment.
Join the discussion