Chinese-Linked TA419 Group Launches Credential Phishing Campaign Against U.S. AI Policy Professionals
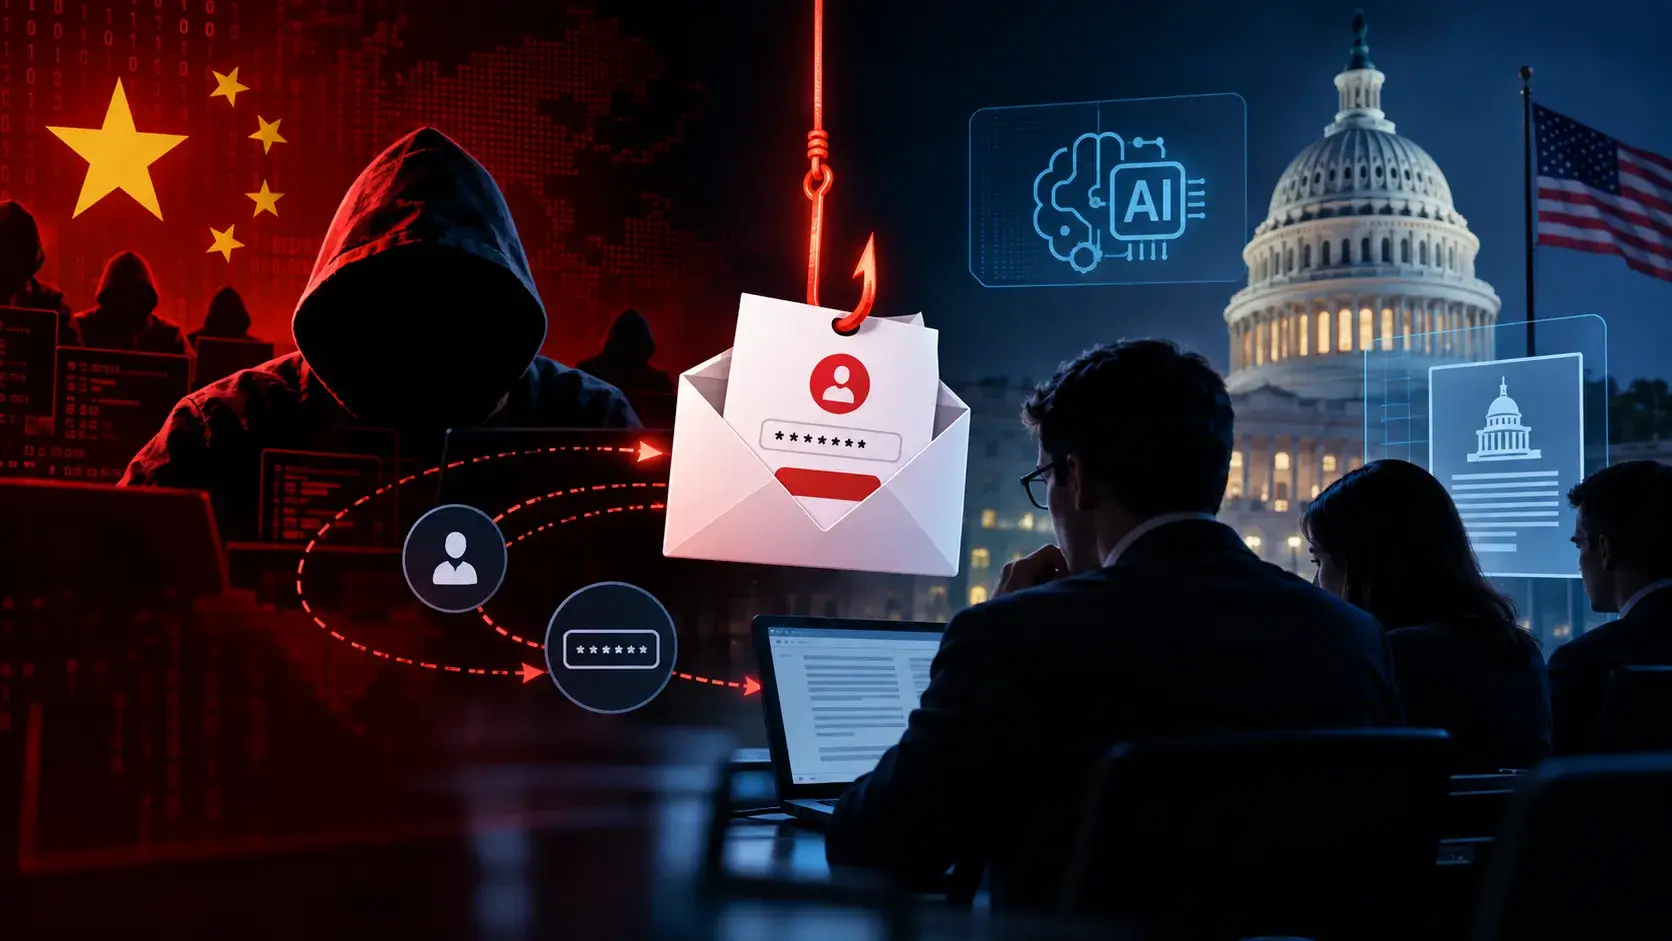
A cyber espionage group identified as TA419, which intelligence analysts link to Chinese state interests, has begun a focused phishing operation aimed at individuals involved in shaping artificial‑intelligence policy in the United States. The campaign relies on highly tailored credential‑stealing messages that appear to come from trusted contacts, seeking to compromise email accounts and internal networks of policy advisers, researchers, and government staff.
According to the security firm that first uncovered the activity, the attackers employ a combination of impersonation tactics and an adversary‑in‑the‑middle (AiTM) framework. By inserting themselves between the victim and legitimate services, the group can capture login details in real time and relay traffic without raising immediate suspicion. The infrastructure appears to be a modified version of tools previously observed in other China‑affiliated operations.
Target selection reflects the growing strategic value of AI policy work, which spans issues from export controls to ethical guidelines for emerging technologies. By gaining access to the communications of policy makers, TA419 could harvest sensitive deliberations, draft language, or even influence the development of regulations that affect both domestic and foreign AI firms.
Experts in cyber‑security and foreign policy note that this approach marks a shift from broader, indiscriminate hacking campaigns to precision attacks on niche expertise. The use of custom‑crafted phishing emails suggests that the group has invested significant reconnaissance to map professional relationships and communication habits within the AI policy community.
U.S. officials have not publicly attributed the attacks to any government, but the pattern aligns with known Chinese efforts to acquire strategic technology intelligence. Agencies are reportedly advising affected individuals to adopt multi‑factor authentication, verify sender identities rigorously, and report suspicious requests through established security channels. The incident underscores the need for heightened vigilance as AI becomes an increasingly contested domain in international security.

Comments (0)
Be the first to comment.
Join the discussion