CastleStealer Malware Evolves to Evade Chromium Encryption and Execute Remote Commands
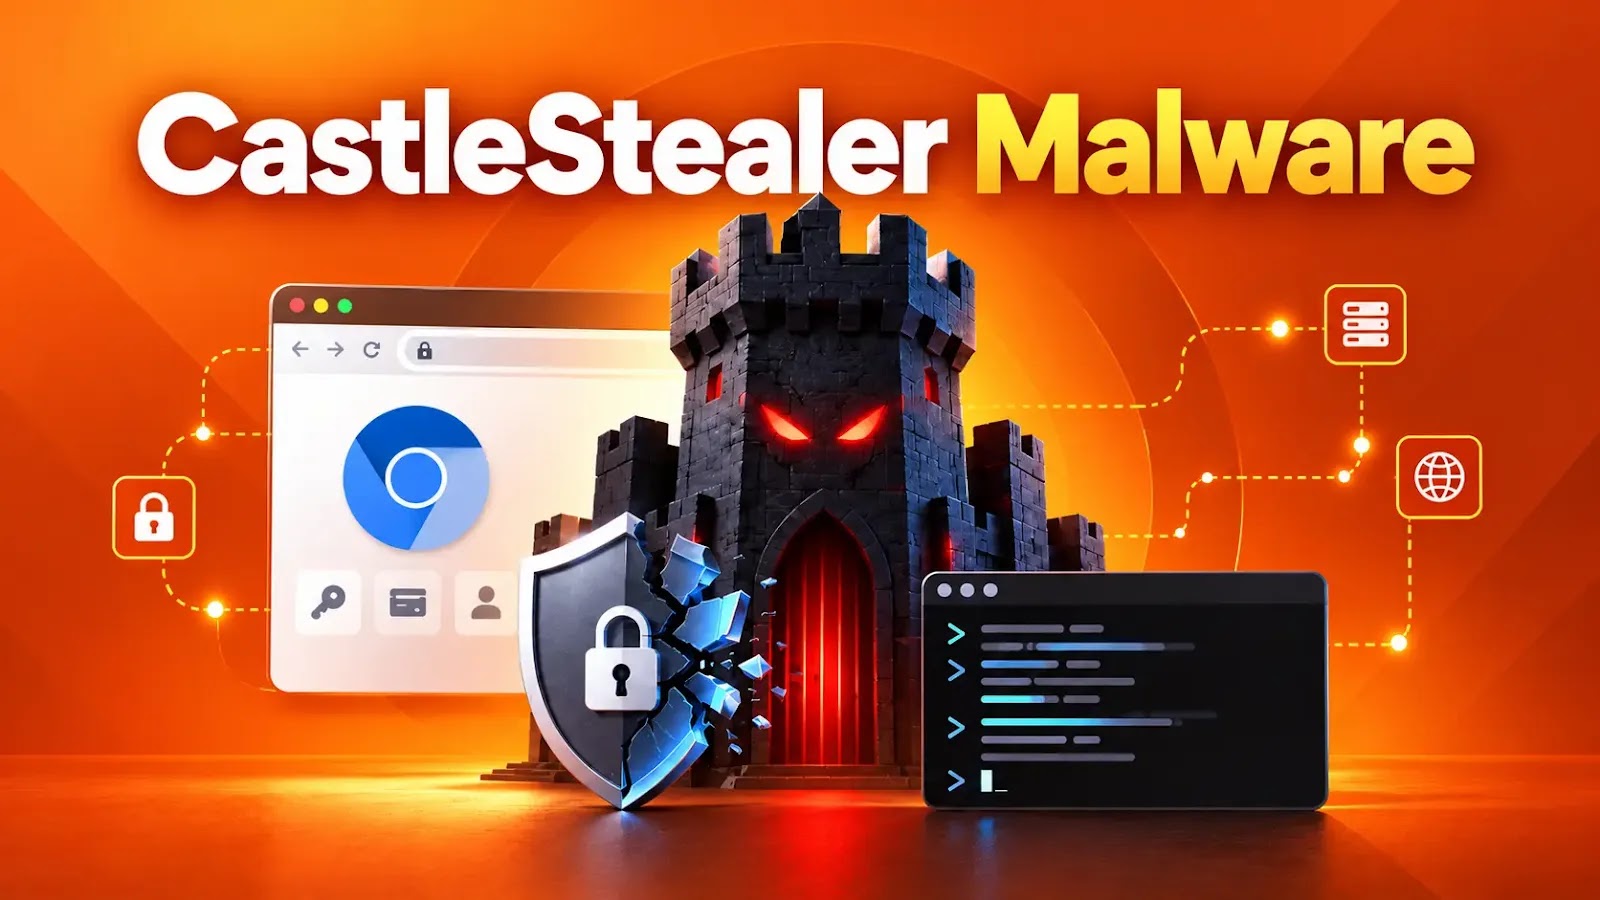
New variants of the CastleStealer information‑stealer have been observed sidestepping Chromium's app‑bound encryption (ABE) while also adding the ability to run commands remotely, security researchers said.
First uncovered in April 2026, CastleStealer is a C#‑based payload that initially focused on harvesting login credentials from compromised systems. Early samples were limited to stealing stored passwords, cookies and other authentication data before exfiltrating them to a command‑and‑control (C2) server.
Analysis by the threat‑intelligence firm Flashpoint shows that the latest code revisions incorporate techniques to neutralize Chromium's ABE, a protection layer that encrypts extension data and browser‑stored secrets. By breaking this encryption, the malware can access a broader set of browser artifacts, including saved form data and session tokens that were previously out of reach.
In addition to the decryption bypass, the updated malware embeds a remote command execution (RCE) module. This component lets attackers issue arbitrary shell commands on infected hosts, turning a passive data‑theft tool into an active foothold for further intrusion or lateral movement within a network.
Stolen information continues to be funneled through the malware's existing exfiltration channel, which employs encrypted traffic to mask the data flow. While the exact transport mechanisms were not disclosed, Flashpoint noted that the traffic blends with legitimate web traffic, complicating detection by conventional network monitors.
The enhancements raise the threat level of CastleStealer for enterprises that rely heavily on Chromium‑based browsers such as Google Chrome, Microsoft Edge or the open‑source Chromium project. Security teams are urged to update endpoint detection rules, monitor for anomalous browser‑related processes, and enforce strict application whitelisting where feasible.
Industry analysts say the evolution reflects a broader trend where information‑stealing malware is being repurposed as multi‑functional intrusion tools. By combining credential harvesting with command execution, threat actors can streamline their attack chain and reduce the need for multiple payloads.
Researchers anticipate that future iterations may integrate additional persistence mechanisms or exploit other browser‑specific defenses. Organizations are advised to stay informed of emerging indicators of compromise and to apply timely patches to both browsers and underlying operating systems.
Comments (0)
Be the first to comment.
Join the discussion