Senate Leaders Propose Telecom Cybersecurity Bill Following Salt Typhoon Revelations
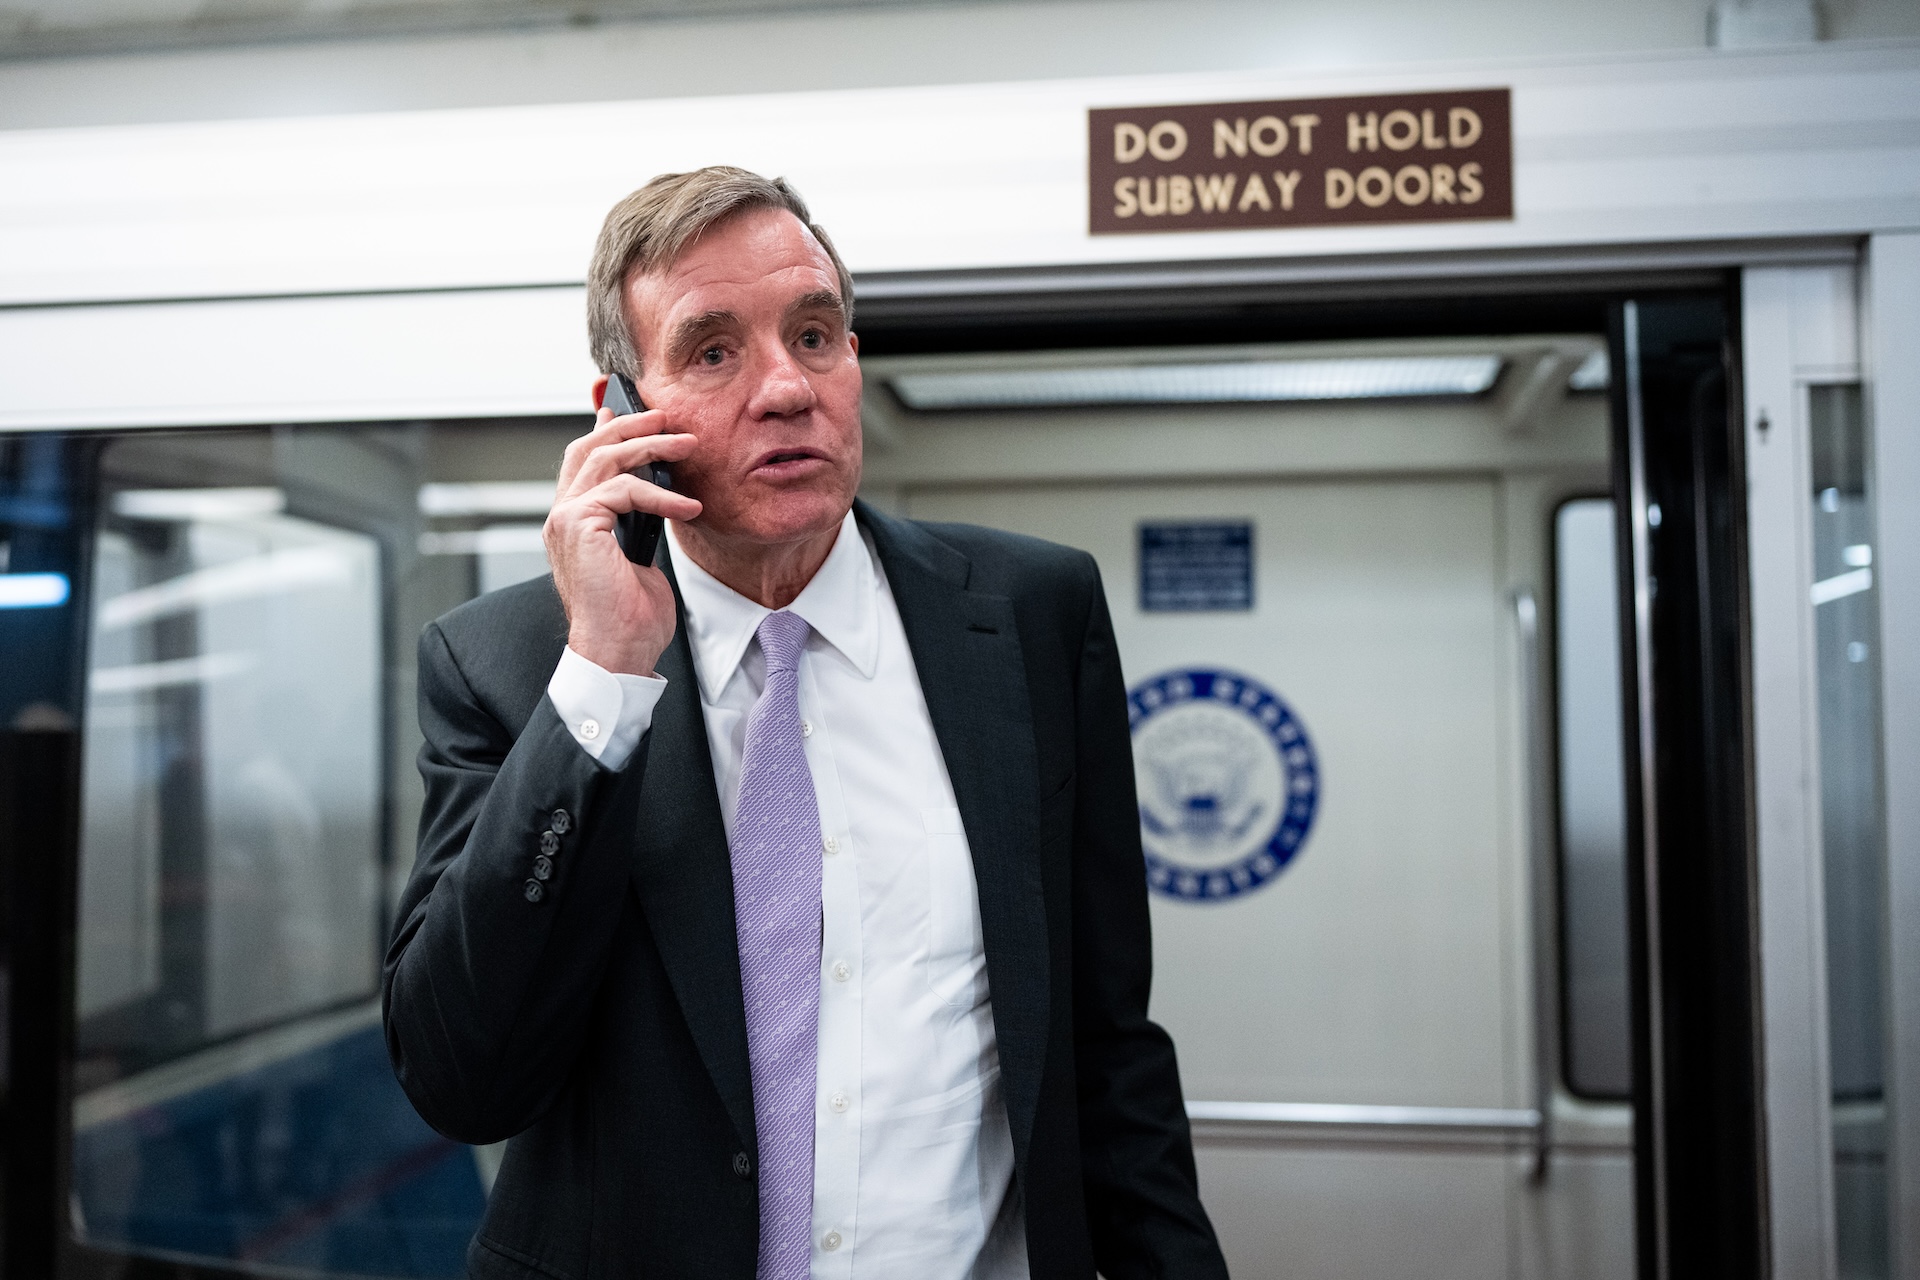
Two senior Senate committee chairs introduced bipartisan legislation this week aimed at establishing uniform cybersecurity standards for the United States telecommunications industry, a move prompted by the fallout from the Salt Typhoon espionage campaign disclosed nearly two years ago.
The bill, announced by Virginia Senator Mark Warner, the leading Democrat on the Senate Commerce Committee, and his Republican counterpart, seeks to create a framework for vulnerability assessments, information‑sharing protocols, and mandatory remediation timelines for carriers and equipment manufacturers.
Salt Typhoon, first reported publicly in 2022, revealed that a sophisticated state‑backed hacking operation had infiltrated the networks of multiple U.S. telecom providers, raising concerns about the resilience of critical communications infrastructure. While the full scope of the breach remains classified, the episode underscored gaps in existing security practices and the need for coordinated federal oversight.
Warner’s proposal builds on earlier, piecemeal efforts by the Federal Communications Commission and the Department of Homeland Security, which have issued advisories and voluntary guidelines but lack enforceable authority. By codifying standards into law, the legislation would empower the FCC to impose penalties for non‑compliance and to require regular reporting on cyber risk mitigation.
Supporters argue that a uniform set of rules will help protect not only consumer data but also national security, given the integral role of telecom networks in emergency response, financial transactions, and defense communications. Industry groups have expressed cautious optimism, noting that clear expectations could reduce uncertainty and streamline investment in security upgrades.
Critics, however, warn that mandatory requirements could impose significant costs on smaller carriers and could stifle innovation if the standards are overly prescriptive. The bill includes provisions for a phased implementation schedule and a grant program to assist smaller operators in meeting the new obligations.
Legislators plan to move the measure through the Senate Commerce Committee before bringing it to the full chamber, with an eye toward inclusion in the broader cybersecurity agenda for the upcoming congressional session. If enacted, the law would represent the most comprehensive federal effort to safeguard the nation’s telecom backbone against foreign and domestic cyber threats.



Comments (0)
Be the first to comment.
Join the discussion