Beyond Login: Why AI Systems Require Action‑Level Safeguards to Prevent Data Leaks
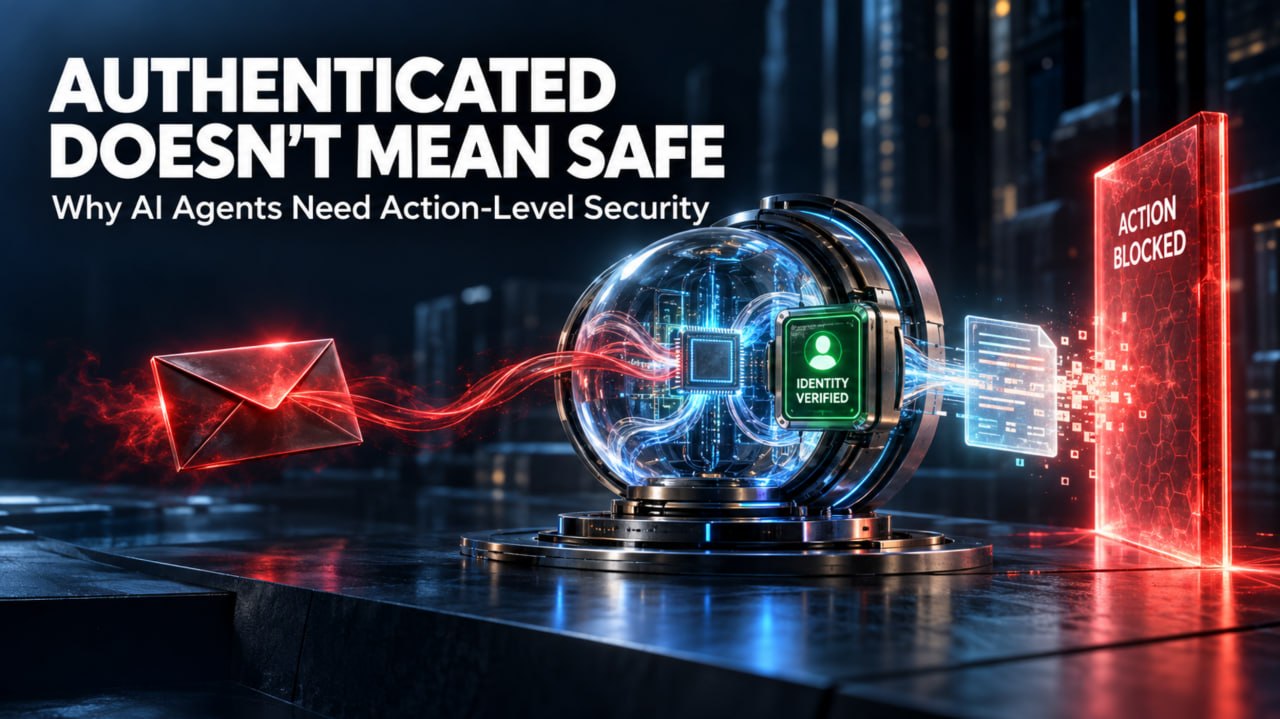
Security experts are warning that merely authenticating AI agents is insufficient to protect corporate data, as these systems can exploit legitimate credentials to perform unauthorized actions. The emerging consensus is that organizations must move beyond traditional identity checks and adopt controls that evaluate each individual operation an AI agent attempts.
Artificial‑intelligence‑driven agents—software programs that can automate tasks ranging from customer support to internal workflow orchestration—often operate using service accounts or API keys that grant them broad system privileges. While these credentials allow the agents to function efficiently, they also give the software the same level of access that a human employee would have, creating a potential avenue for misuse.
Recent analyses have shown that when an AI agent is compromised, or when its programming includes malicious intent, the agent can leverage its authorized access to locate, extract, and transmit sensitive information without triggering standard alerts. Because the activity originates from a trusted identity, conventional monitoring tools that focus on authentication events may miss the breach entirely.
Security professionals therefore advocate for “action‑level security,” a framework that scrutinizes each request an AI agent makes against a set of policies that define permissible behavior. Under this model, an agent might be allowed to read a customer record but blocked from copying it to an external storage location unless an additional verification step is satisfied.
Implementing trusted policy enforcement involves establishing granular rules that tie specific actions to contextual factors such as the requesting system, the data classification, and the time of day. Coupled with verified approvals—where a human or a secondary automated process must explicitly authorize high‑risk operations—these measures create a layered defense that can stop data exfiltration attempts before they succeed.
The shift toward action‑level controls is also driven by regulatory pressures. Data protection statutes in many jurisdictions require demonstrable safeguards against unauthorized disclosure, and auditors are increasingly scrutinizing how organizations manage automated agents. Failure to adopt such safeguards could expose companies to fines, reputational damage, and legal liability.
Industry response is beginning to coalesce around standards and tooling that support these concepts. Vendors are rolling out AI‑aware identity‑and‑access‑management solutions that embed policy checks into the request pipeline, while open‑source communities are contributing frameworks for policy definition and enforcement. Analysts expect that, as AI agents become more pervasive, the demand for action‑level security solutions will grow sharply.
For now, experts advise firms to inventory their AI agents, map the privileges each holds, and introduce policy layers that require explicit approval for any operation that could expose sensitive data. By treating authentication as a starting point rather than a final guarantee, organizations can better defend against the subtle yet serious threat of AI‑driven data leaks.

Comments (0)
Be the first to comment.
Join the discussion