Supply‑Chain Threats Shift Toward Cloud Identity Theft via Compromised Developer Tools
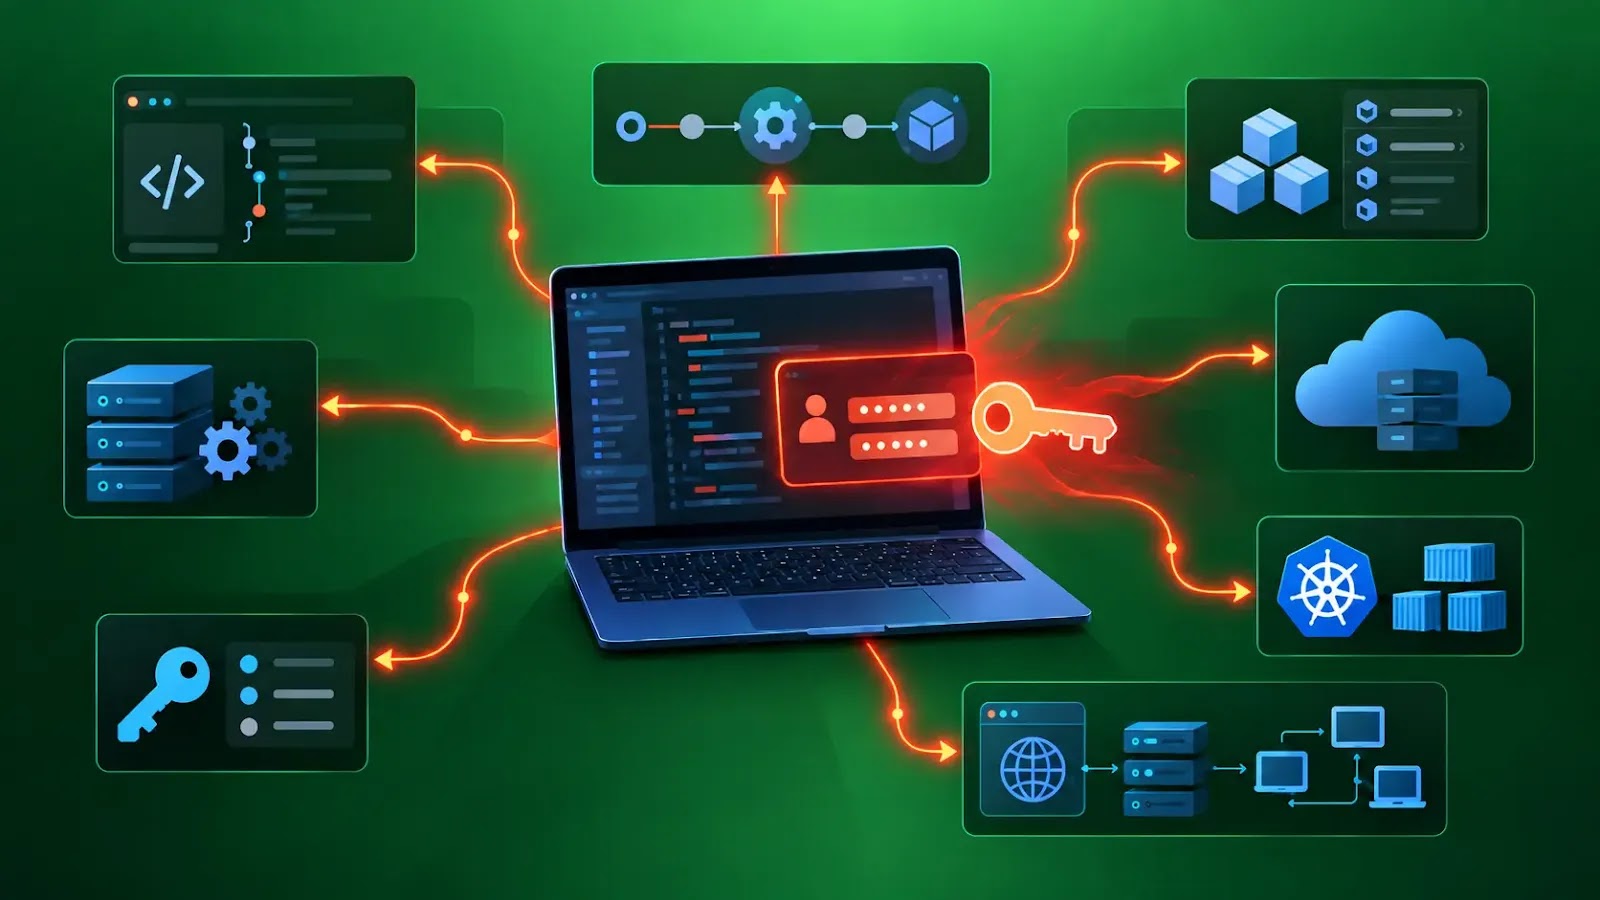
Cyber‑criminals are broadening the scope of software supply‑chain attacks by moving beyond malicious code injection to direct theft of developer credentials, a trend that enables deeper infiltration of cloud environments before any application is even run.
Recent analyses show that attackers are weaponizing widely‑used open‑source packages to gain footholds on developer workstations and continuous integration/continuous deployment (CI/CD) pipelines. By embedding covert payloads in trusted libraries, they can capture authentication tokens, SSH keys, and API secrets stored on the machines that build and ship software.
Once these credentials are exfiltrated, the threat actors can impersonate legitimate developers, access version‑control repositories, and pivot into cloud services such as container registries, serverless platforms, and infrastructure‑as‑code tools. This “identity‑first” approach sidesteps many of the traditional defenses that focus on scanning binaries for malicious code, making detection considerably harder.
Industry observers note that the shift reflects the growing reliance on cloud‑native development workflows, where developers routinely log into cloud consoles and store secrets in environment variables or secret‑management services. Compromise of a single developer account can therefore grant attackers broad, persistent access to production resources, data stores, and downstream services.
Security teams are responding by tightening controls around credential handling in development environments. Recommendations include enforcing short‑lived, scoped tokens, integrating secret‑scanning tools into CI pipelines, and adopting zero‑trust policies that limit the privileges of build agents. Some organizations are also moving toward isolated, hardened build environments that restrict network access during compilation.
Analysts warn that as attackers refine these techniques, the line between supply‑chain sabotage and outright cloud infrastructure breach will continue to blur. Ongoing vigilance, improved tooling for credential leakage detection, and a cultural shift toward “security‑by‑design” in the software development lifecycle are seen as essential steps to curb the emerging threat vector.


Comments (0)
Be the first to comment.
Join the discussion