ASOS probes breach after shoppers receive warning of possible data leak
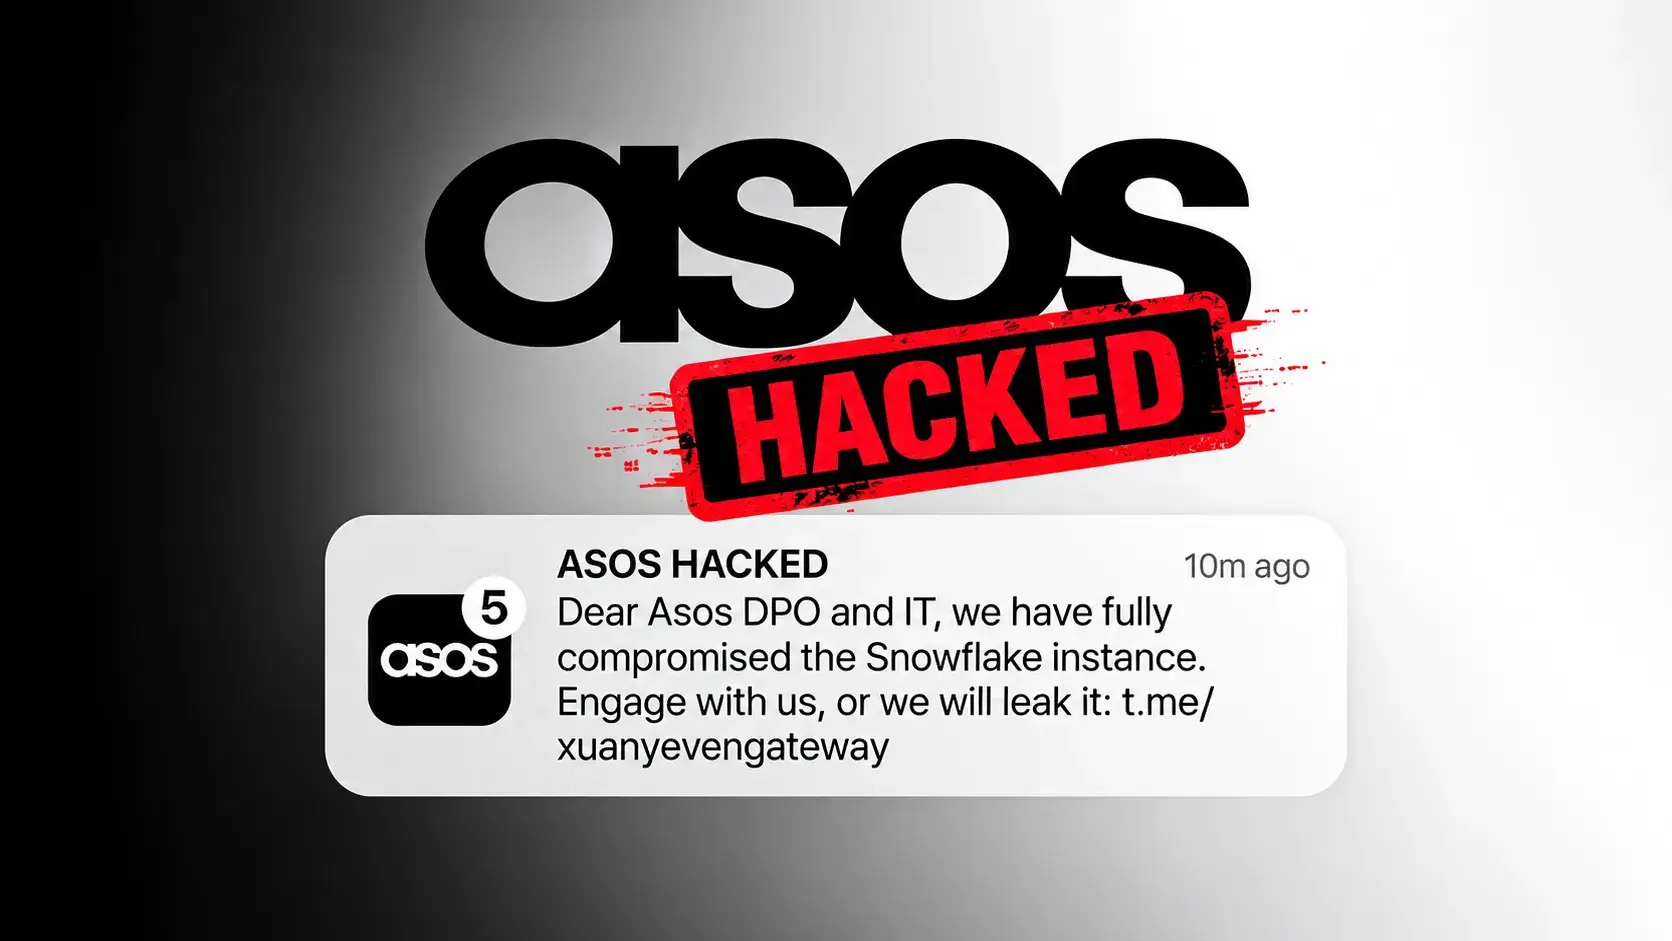
Online fashion retailer ASOS has launched an investigation after a number of customers reported receiving an unexpected notification through the company’s mobile app warning of a potential data breach. The alert, which appeared to be generated by a third‑party communication service, claimed that attackers had accessed ASOS’ Snowflake data‑warehouse environment and threatened to expose customer information.
According to reports, the push notification arrived on users’ devices without any prior indication of a problem, urging recipients to review their accounts for suspicious activity. Recipients shared screenshots on social media, prompting immediate concern among shoppers and security observers. ASOS has not confirmed that any data was actually compromised, but the message has raised questions about the security of the retailer’s supply‑chain partners.
Industry analysts note that the notification likely originated from a third‑party platform used by ASOS to manage customer communications, a common practice that can expand the attack surface of large e‑commerce operations. Snowflake, a cloud‑based data‑warehouse service, stores large volumes of transactional and personal data for many retailers. While the attackers alleged access to this environment, ASOS has said it is reviewing logs and working with the service provider to verify the claim.
In a statement released on its website, ASOS said it is treating the incident as a serious security event, has engaged external cyber‑security experts, and is cooperating with law‑enforcement agencies. The company emphasized that there is no evidence at this stage that any personal data has been extracted or misused, and it is advising customers to monitor their accounts for any unusual activity.
The episode underscores a broader trend of supply‑chain attacks, where threat actors target less‑protected vendors to gain indirect access to larger organizations. Recent incidents involving other retailers and service providers have highlighted the need for robust vetting and continuous monitoring of third‑party tools. Regulators in the UK and EU have been urging firms to strengthen their data‑protection practices, especially after the implementation of stricter privacy legislation.
ASOS has pledged to update customers as the investigation progresses and to implement additional safeguards on its communication channels. Security experts recommend that affected users change passwords, enable two‑factor authentication, and remain vigilant for phishing attempts that often follow such disclosures. The outcome of the probe will likely shape the retailer’s future approach to third‑party risk management and could influence industry standards for handling similar threats.

Comments (0)
Be the first to comment.
Join the discussion