Small Security Teams Get a Boost with Seven Top Vulnerability Scanners for 2026
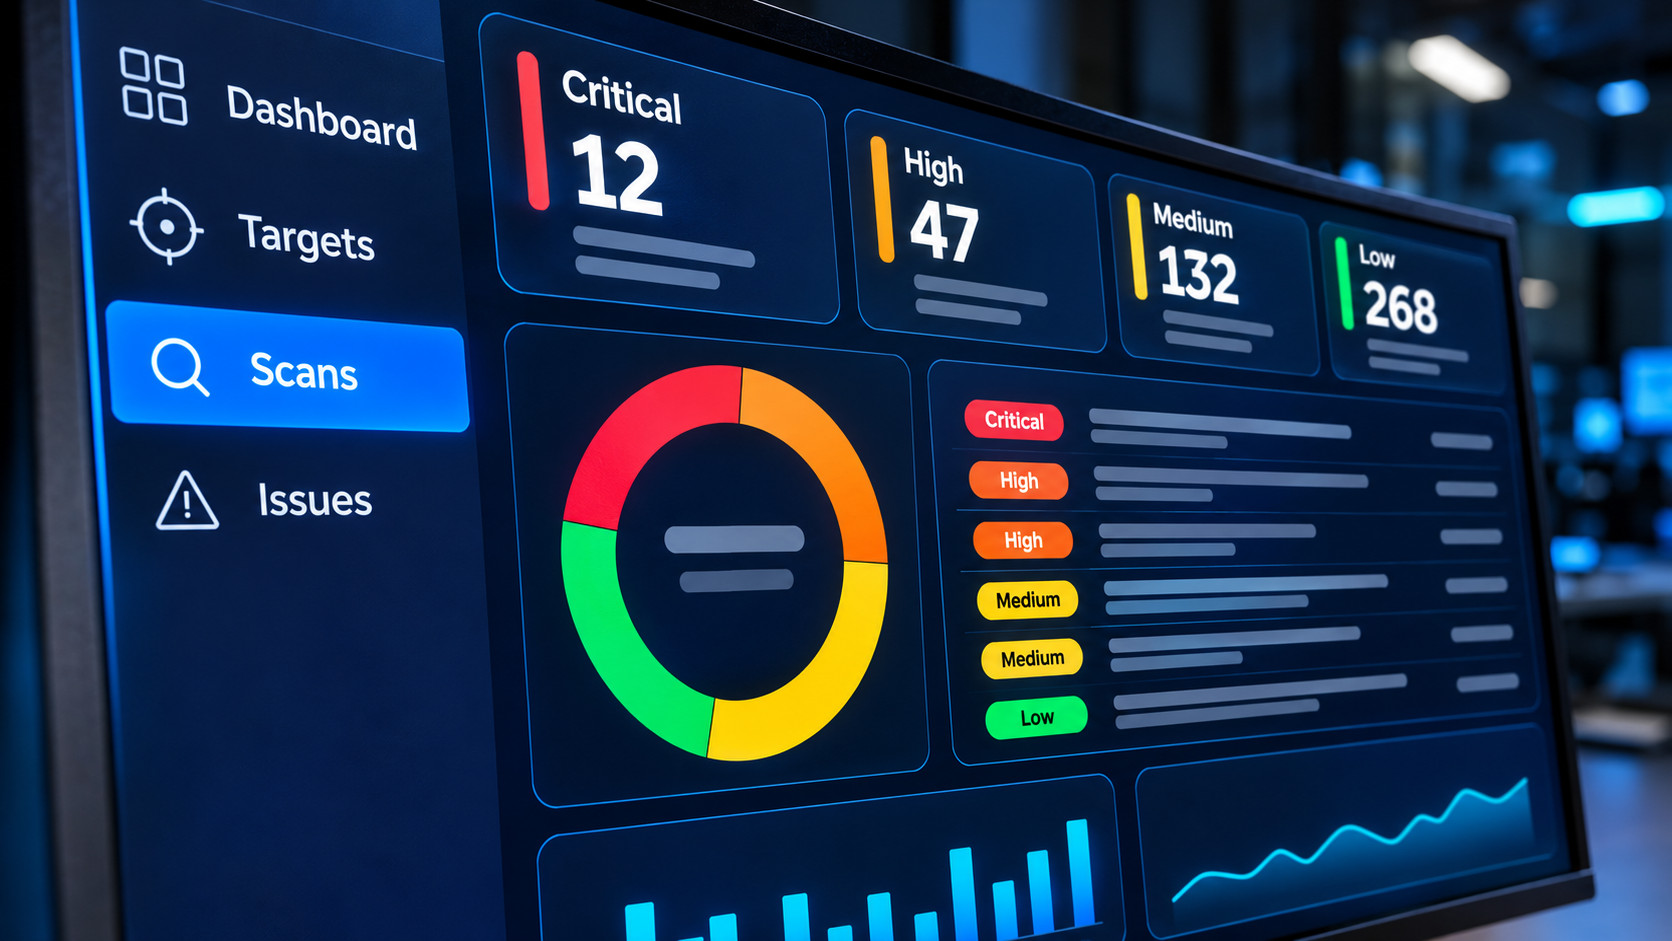
In a landscape where cyber threats continue to outpace many organizations' defenses, a new roundup from Hackread highlights seven vulnerability scanning tools that are especially suited to lean security teams. The selection emphasizes ease of deployment, coverage of both network and application layers, and built‑in features for prioritising findings, automating rescans, and tracking remediation progress.
The tools evaluated span open‑source projects and commercial platforms, each offering a relatively low barrier to entry. Reviewers noted that initial setup can be completed in a matter of hours, a critical factor for teams that lack dedicated infrastructure staff. Many of the solutions integrate with common ticketing systems, allowing alerts to flow directly into existing workflow tools without manual hand‑off.
Beyond basic scanning, the comparative analysis stresses the importance of intelligent prioritisation. Modern scanners now assign risk scores based on exploitability, asset criticality, and contextual factors, helping small teams focus on the most pressing vulnerabilities first. Several of the highlighted products also feature automated rescan schedules, ensuring that patched systems are re‑tested and that new gaps are identified promptly.
Remediation tracking emerged as another differentiator. While traditional scanners often stop at reporting, the tools on Hackread’s list provide dashboards that map findings to remediation tickets, record status changes, and generate compliance reports. This capability reduces the administrative overhead for understaffed teams and supports audit requirements across industries such as finance, healthcare, and retail.
Analysts predict that as the talent shortage in cybersecurity persists, the demand for solutions that combine simplicity with depth will keep growing. The seven scanners reviewed are positioned to meet that demand, offering small teams a pragmatic way to maintain a continuous vulnerability management program without the need for large budgets or extensive specialist expertise. Organizations are encouraged to pilot multiple options to determine which aligns best with their existing tech stack and risk profile, keeping an eye on future updates that may further streamline the vulnerability lifecycle.


Comments (0)
Be the first to comment.
Join the discussion