Firefox Users Targeted by Malicious Extensions Masquerading as Crypto Wallets
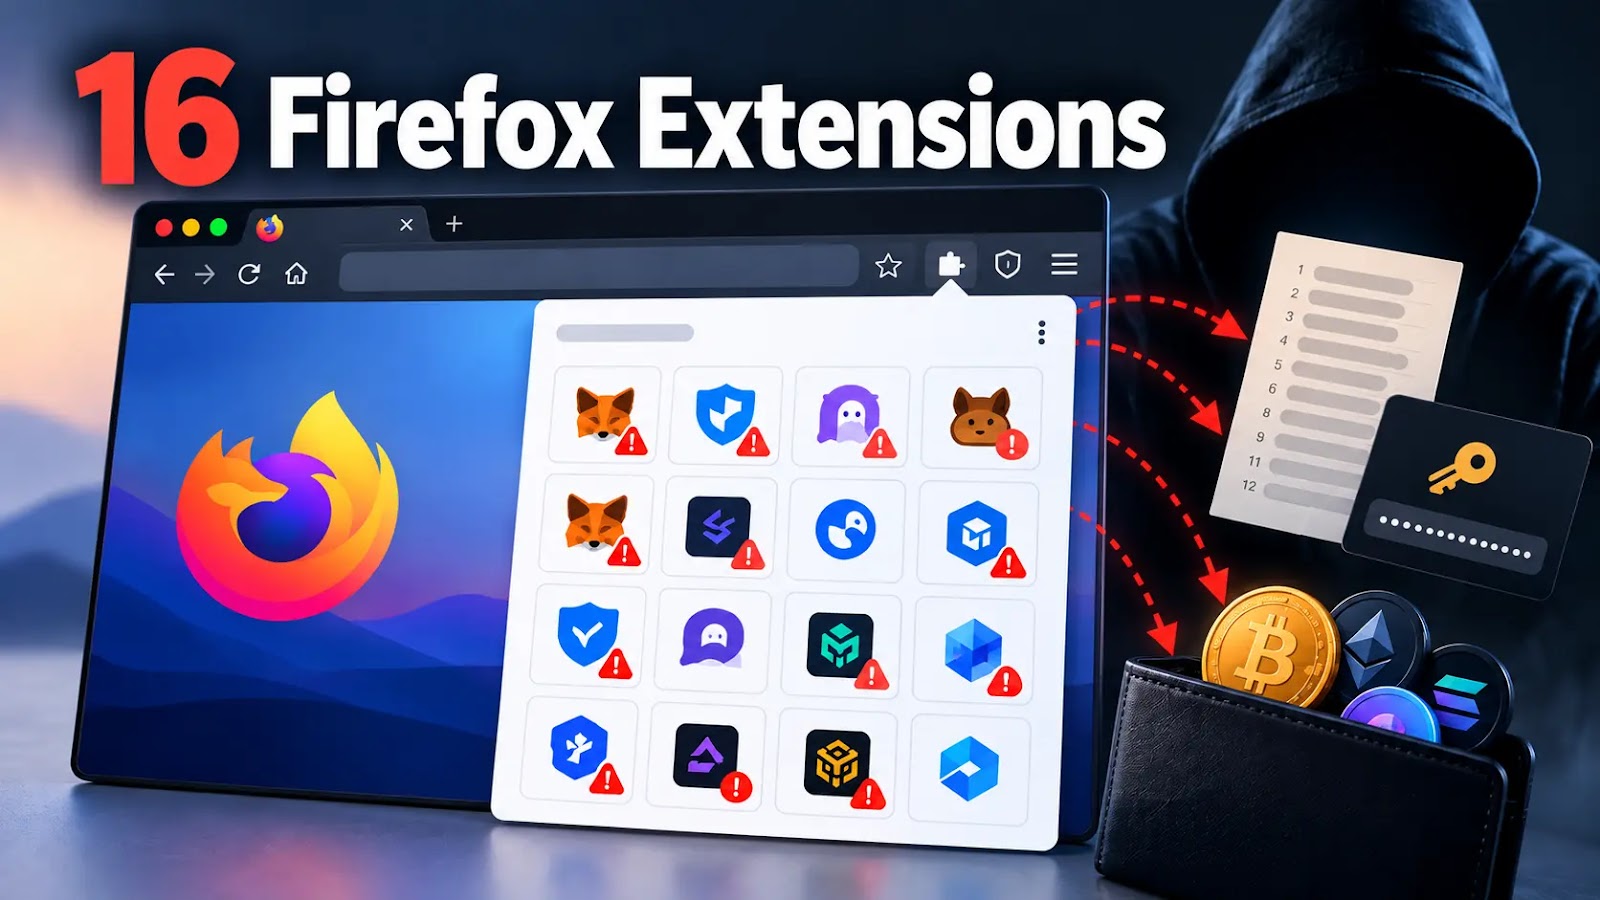
Security researchers have uncovered a coordinated campaign involving sixteen Firefox add‑ons that pose as cryptocurrency wallet interfaces. The extensions are designed to capture seed phrases and private keys when users attempt to import or restore their digital assets, then silently forward the stolen data to servers controlled by the attackers.
According to the analysis, the malicious packages are distributed under a variety of guises—some appear to be official wallet portals, others claim to be desktop utilities for managing crypto, and a few present themselves as generic browser tools. Once installed, the extensions monitor the pages where wallet recovery phrases are entered and duplicate the information, transmitting it to remote endpoints before allowing the user to continue.
The technique exploits a fundamental trust model in browsers: users often assume that extensions listed in official stores have been vetted. Firefox’s extension review process, while robust, can be circumvented by cleverly crafted code that only activates under specific conditions, such as the presence of a wallet import form. By mimicking legitimate user interfaces, the malicious add‑ons increase the likelihood that victims will unwittingly disclose their most sensitive credentials.
Experts warn that the impact could be severe for individuals and small investors who rely on browser‑based wallets for convenience. Unlike hardware wallets, which keep private keys offline, software wallets accessed through a browser are inherently more exposed. The theft of a seed phrase grants an attacker full control over the associated blockchain accounts, enabling the rapid siphoning of funds that are often irrecoverable.
The discovery underscores the ongoing need for vigilance when installing browser extensions, especially those related to financial services. Users are advised to verify the publisher’s identity, read reviews, and limit the number of crypto‑related add‑ons to those that are essential. Firefox has been notified of the findings and is expected to remove the offending extensions from its repository. Meanwhile, security firms continue to monitor the threat landscape for similar campaigns targeting other browsers and platforms.

Comments (0)
Be the first to comment.
Join the discussion